Documentation ready for your
compliance audits
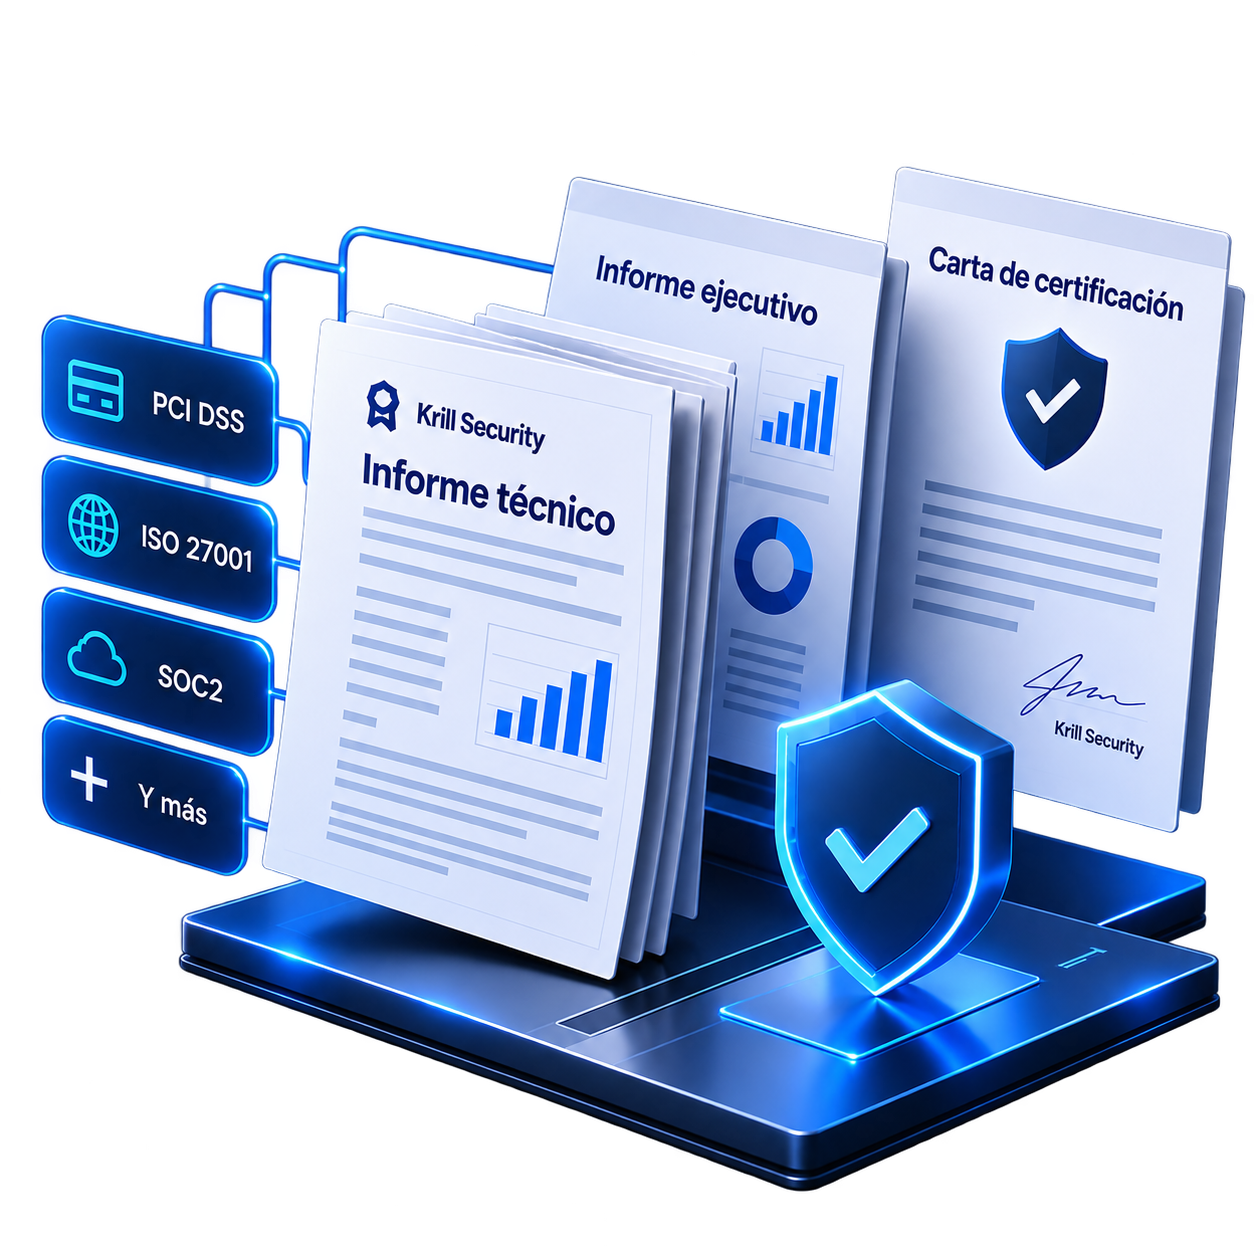
We deepen the autonomous pentest with a manual expert review and deliver compliance-ready documentation: a technical report, an executive report, and a certification letter backed by Krill Security, ready to hand over in audits such as PCI DSS, ISO 27001, SOC 2, and more.
Validated by people, backed by Krill Security
Our specialists take the findings from the autonomous pentest, deepen the exercise by hand, and consolidate everything into an audit-ready certificate.
Manual validation
A security specialist reviews every relevant finding, discards false positives, and deepens the exercise to confirm real impact.
Technical report
Detailed documentation of each vulnerability, with exploitation evidence, affected assets, and remediation guidance for your team.
Executive report
A clear summary of the security posture and residual risk, ready to share with leadership, clients, or investors.
Certification letter
A letter backed by Krill Security attesting the assessment was performed, usable in certification processes such as PCI DSS, ISO 27001, SOC 2, and more.
Understand your security exposure.
If you're looking for an alternative to traditional application security, fill out the form and a specialist will explain how Krill can help you maintain ongoing visibility into your attack surface. Our team will respond within the next few hours.
Or reach us directly at hello@krillsecurity.com
hello@krillsecurity.com